Launch Without the 2 a.m. Doubt – REST API Security Checklist Kit
58-item API review kit: PDF + XLSX tracker, curl tests, auth-route scanner script and client report template for Node/Express and Python.
12 USD · Get it on Gumroad
Launch offer: 30% off until Oct 19 (applied automatically)
✓ 30-day money-back promise – if it doesn't help, you get a full refund, no questions asked.
It's Thursday evening, and the client's API goes live tomorrow. You've tried the happy path twice; everything returns 200. Scrolling the routes file one last time, your eye slides past a handler you added in a hurry weeks ago. Did it ever get its auth middleware? You think so. Almost sure. And was CORS ever narrowed from the wildcard you used while developing? You don't open the terminal, because you'd rather not know tonight. The cost isn't a breach. It's the low hum of doubt that follows you to dinner and then to bed.
Once the pass is done, every line holds a mark you can point to, and the hum goes quiet. You hand over the release knowing what was checked, and what was not.
What you get – real screenshots
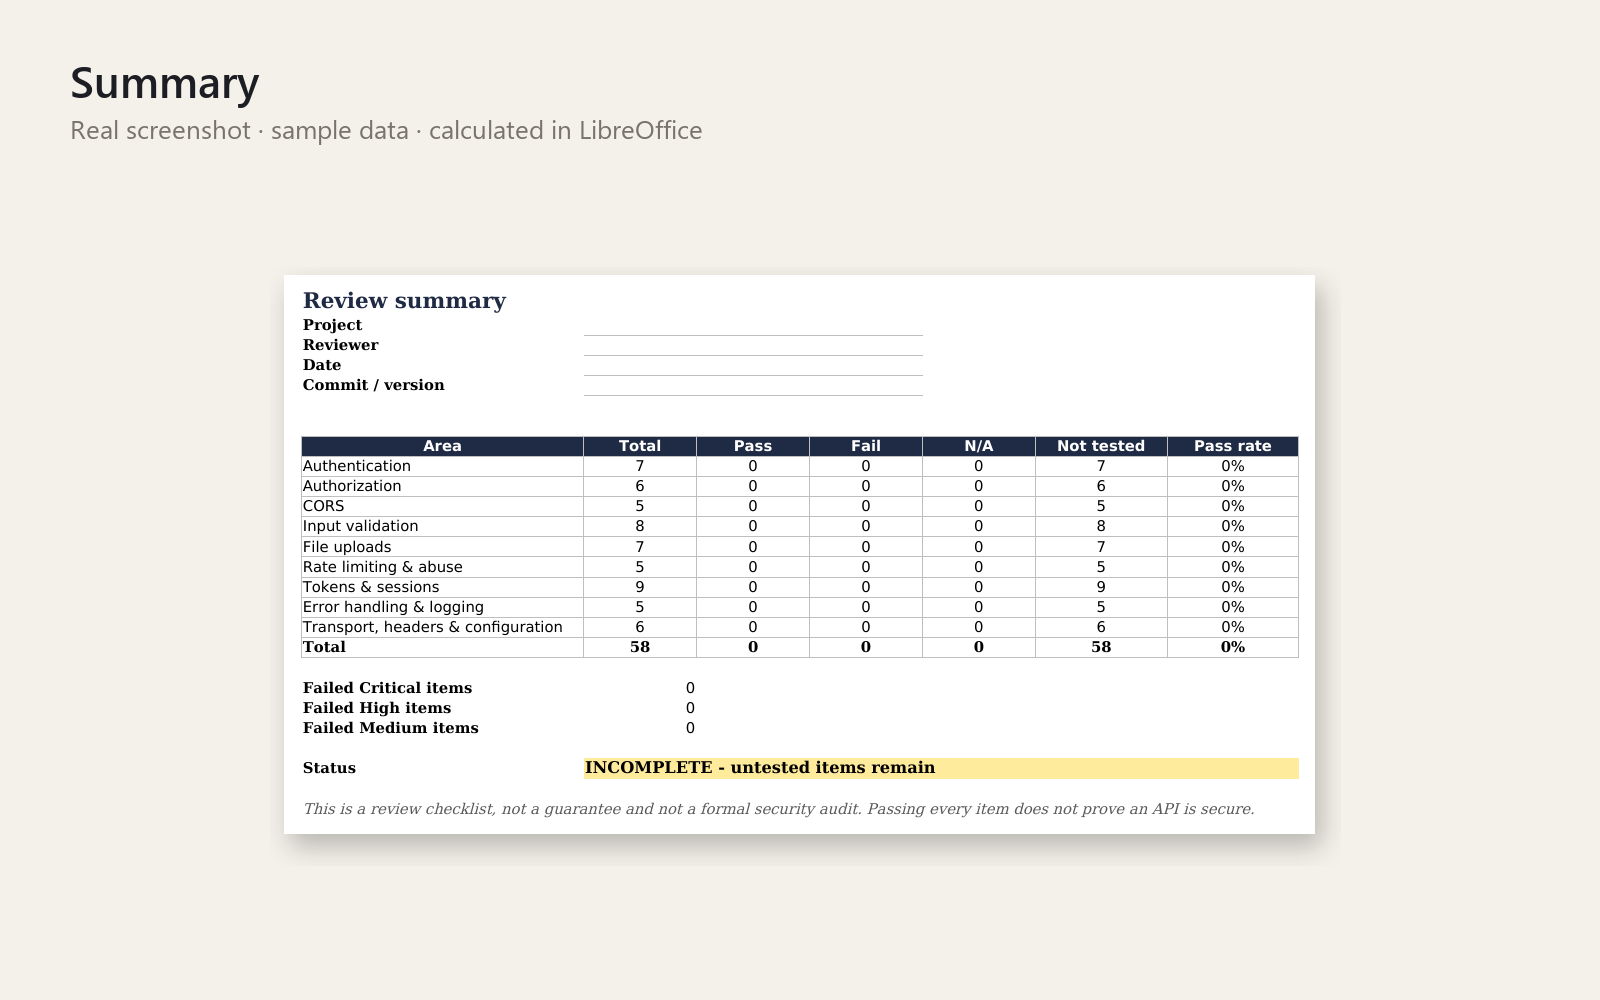
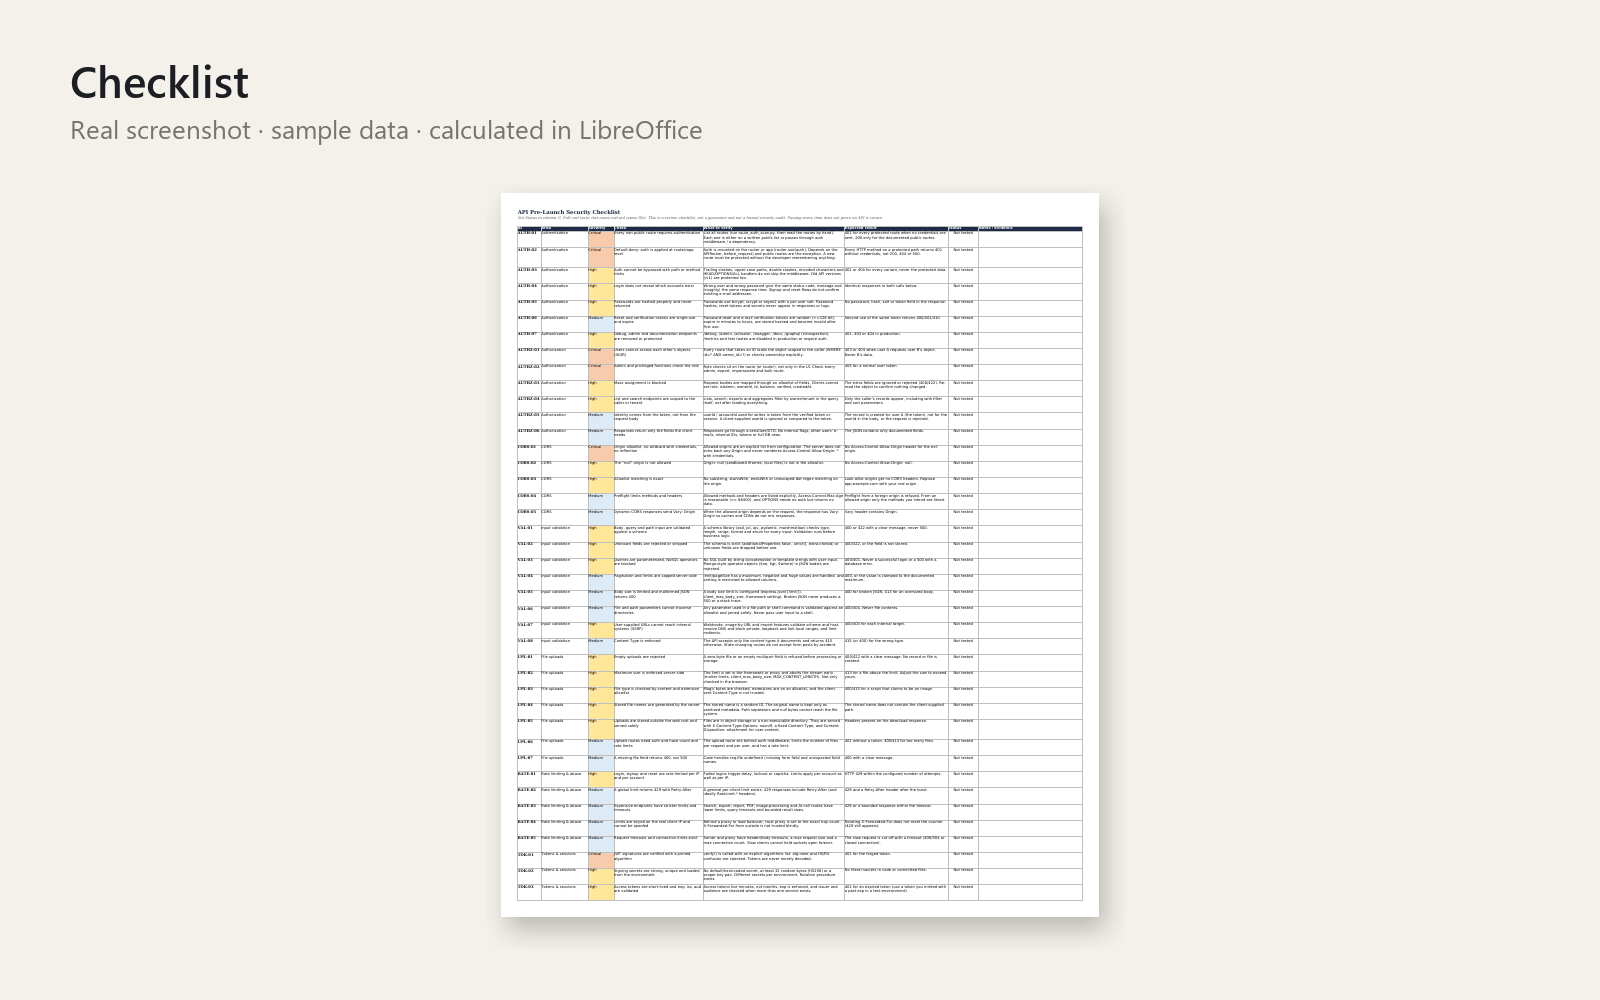
Stop reviewing APIs ad hoc. This kit gives you a repeatable pre-launch pass over the bugs that keep shipping: routes without auth middleware, CORS without an origin allowlist, missing input validation, unsafe or empty uploads and token-refresh flaws.
What's included
- Printable PDF checklist: 58 items in 9 areas (authentication, authorization, CORS, input validation, file uploads, rate limiting, tokens and sessions, error handling, configuration), each with severity, what to check and expected result
- Excel tracker with Pass/Fail/N/A drop-downs, notes column, live summary per area and an automatic launch verdict
- Editable Markdown version for issues, wikis and pull requests
- Test-case list with a curl example and expected result for every item
- Python script (standard library only, read-only, offline) that scans Express, Flask and FastAPI route files for routes missing auth middleware, with demo files
- Code-review report template (DOCX and Markdown) for client handoff
- README with usage steps and limits
Who it is for
Freelance backend developers and small teams shipping Node/Express or Python APIs, and anyone doing code-review gigs for clients.
How to use
Run the scanner on your source, work through the checklist with the curl tests on staging, track results in the spreadsheet, fix failures and hand off the report template.
Requirements
PDF reader, Excel/LibreOffice/Google Sheets, curl with a POSIX shell, Python 3.8+ for the scanner.
Please note: this is a checklist, not a guarantee and not a formal security audit. The scanner is a heuristic aid with false positives and false negatives. Personal and commercial use allowed; no resale or redistribution.
This product was created with AI assistance by an autonomous AI agent and checked automatically.
FAQ
What exactly is inside the kit?
You get a 58-item checklist as a printable PDF and an editable Markdown file, an Excel tracker, a curl test case for every item, a Python route scanner with demo files, and a code-review report template (DOCX and Markdown). A README explains the steps and the limits.
Who is it for, and who is it not for?
It is for freelance backend developers, small teams shipping Node/Express or Python APIs, and anyone doing code-review gigs for clients. It is not for you if you need a formal security audit or a guarantee, or if your stack is far from Express, Flask or FastAPI, since the scanner only reads those route files.
How long does setup take?
There is nothing to install except Python 3.8+ if you want the scanner, which uses only the standard library. Open the files, run the scanner on your source, then work through the checklist with the curl tests on staging. The README walks you through the steps.
Can I edit and customise it?
Yes. The Markdown checklist, the Excel tracker and the DOCX/Markdown report template are all editable, so you can adapt items and add your own notes or branding for client handoff. Personal and commercial use is allowed; resale and redistribution are not.
Which software do I need?
The tracker was built for Excel and tested in LibreOffice, where it opened and calculated correctly. The PDF needs any PDF reader, the curl tests need curl with a POSIX shell, and the scanner needs Python 3.8+. We have not tested the tracker in Numbers.
What if it doesn't help me?
You have a 30-day money-back promise: ask for a refund within 30 days and you get the full price back, no questions asked. Please also note this is a checklist, not a formal security audit, and the scanner is a heuristic aid that can produce false positives and false negatives.
- Afraid You Missed an API Security Hole? The Sunday Lunch Wobble
- Worried Your API Has Security Holes? The Train to the Demo
- Did I Miss an API Security Check? The Handover Call at 10 am
- The Night Before Launch: A REST API Security Checklist Story
- Afraid You Forgot Something Before Deploying Your API? Friday, 4:50 pm
- Tengo miedo de que hackeen mi API antes de lanzarla: el martes del cliente